DNSM
Toolkit for data exfiltration via DNS
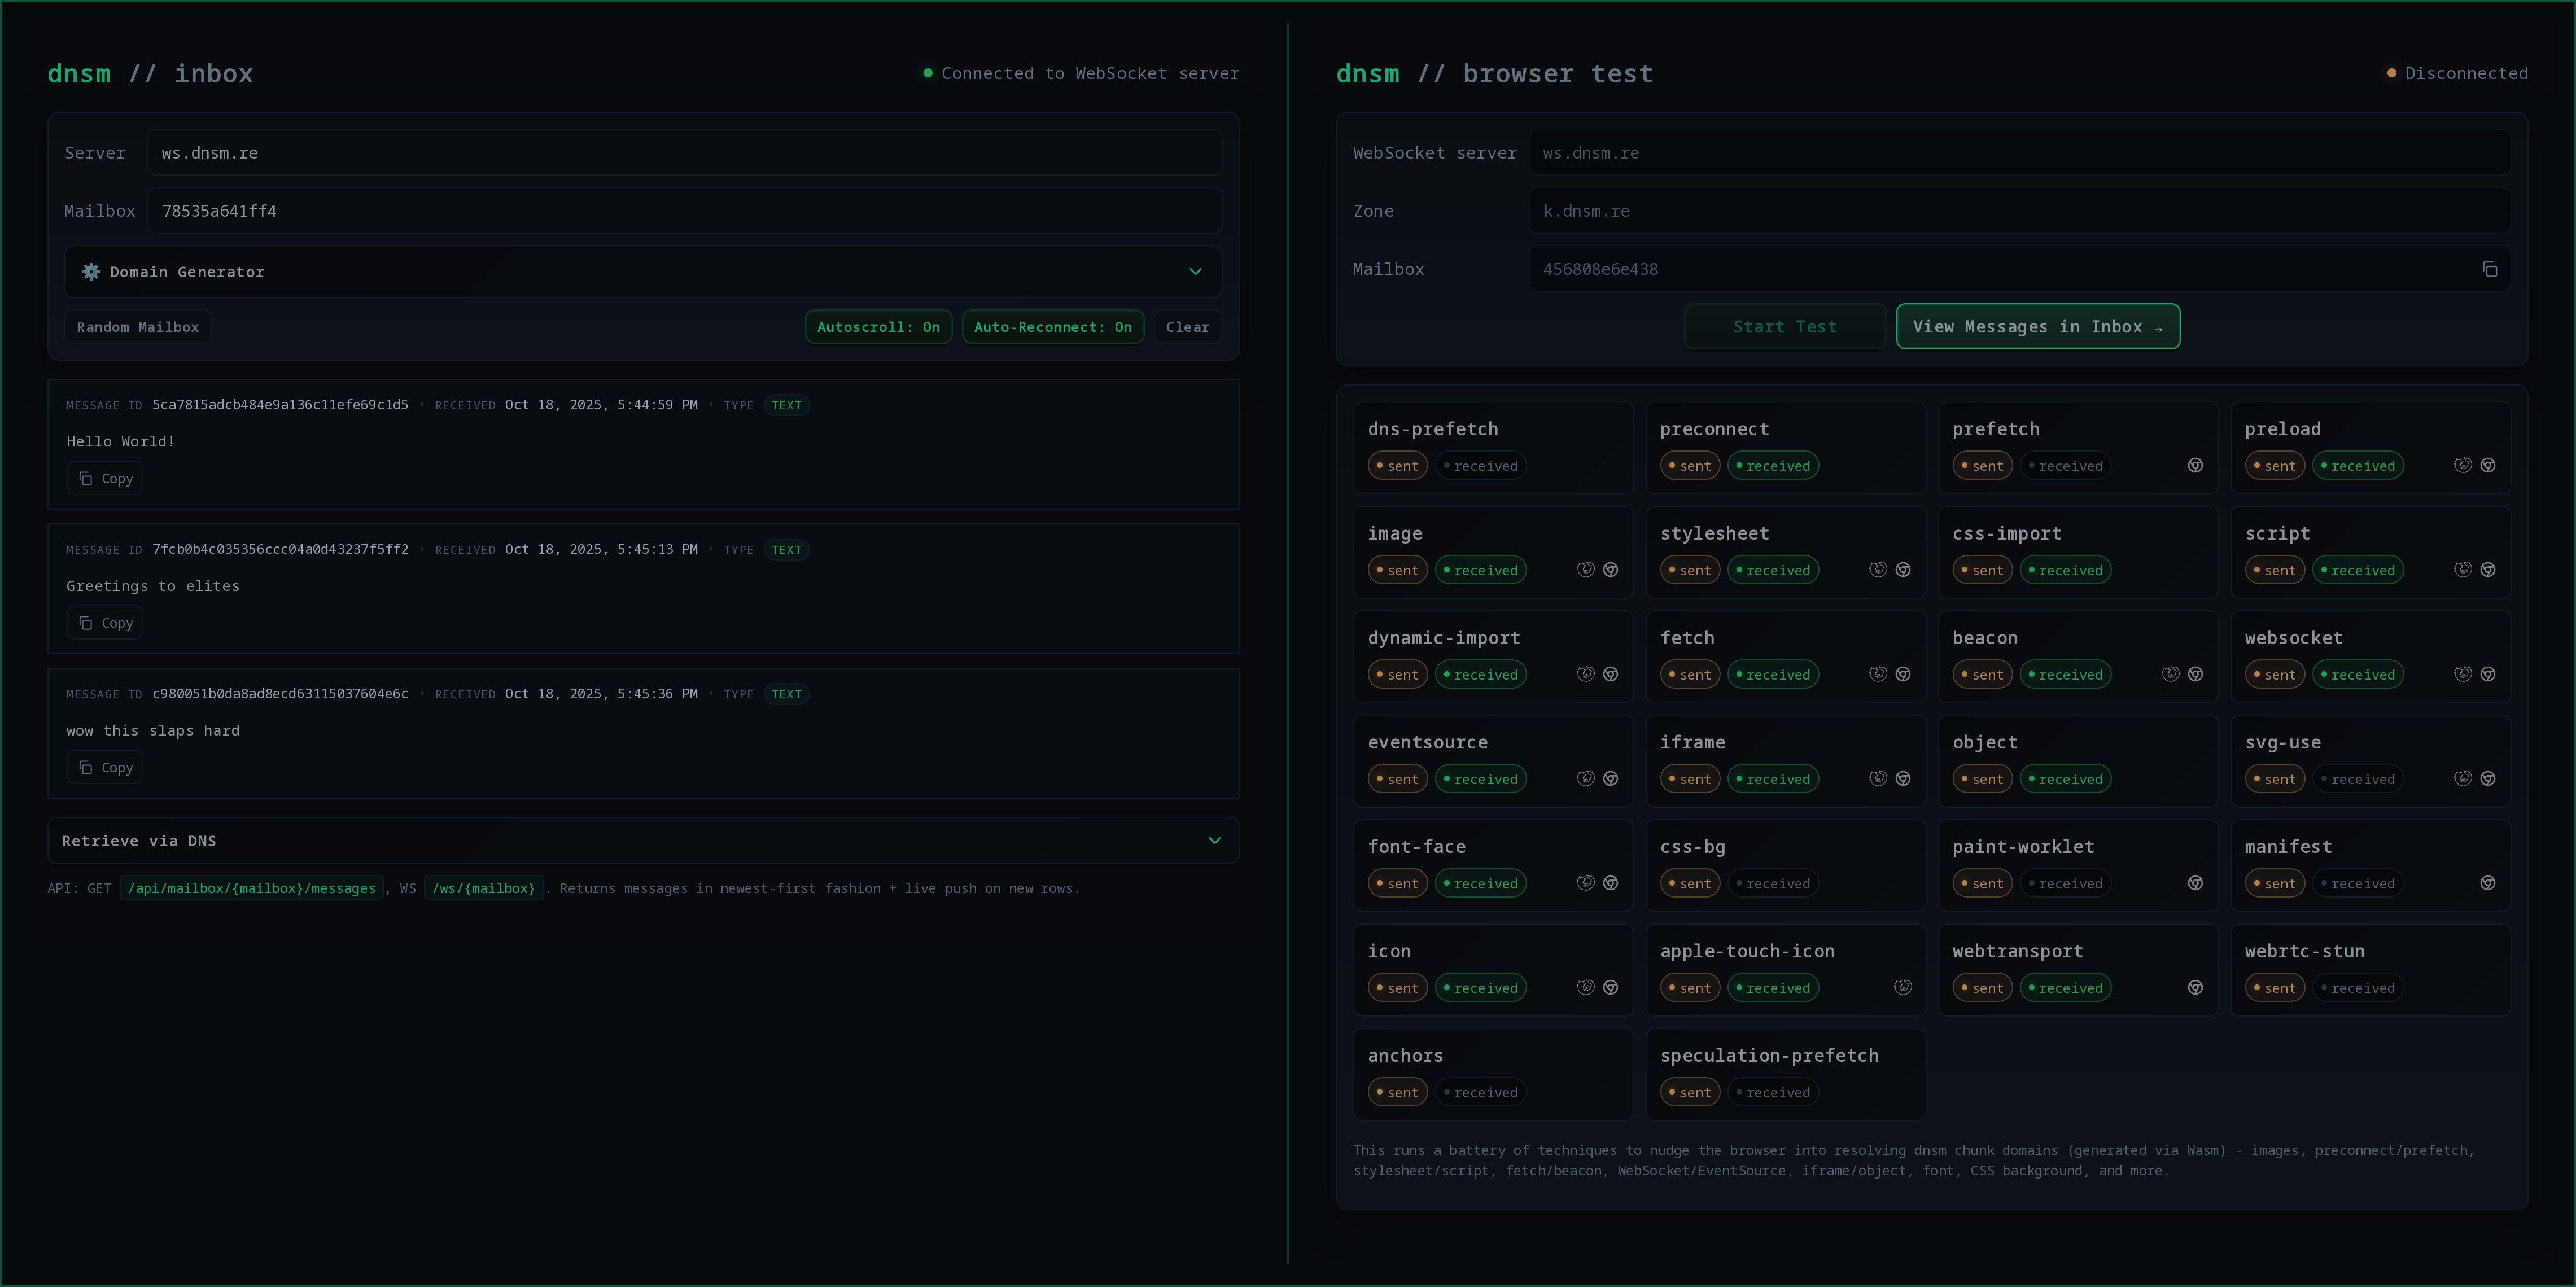
From the site description:
Many environments block outbound TCP/HTTP but leave DNS resolution untouched -- firewalls, proxies, sandboxed runtimes, CI runners, browsers. DNS queries happen early in connection setup, before transport-level controls kick in, and a query can traverse the network even when no subsequent connection is possible.dnsm exploits this: it encodes bytes into the labels of a domain name (think encoded_payload.k.dnsm.re) and lets recursive resolvers carry that name to a zone you control. The server reassembles chunks and decodes the original payload.The protocol: inputs are LZMA-compressed, framed with headers, split into ordered chunks, and base32-encoded into valid hostname labels. Optional mailboxes provide inbox-style retrieval and multiplexing across messages and senders.
Primary source: https://github.com/k-o-n-t-o-r/dnsm